The Perfect System… Until It Wasn’t.
It’s 2 AM. Again. The only things keeping me company are the hum of the server rack and a dangerously cold cup of coffee. For weeks, my new automation pipeline was flawless. A thing of beauty. Data flowed from my AI tools, through n8n, and landed perfectly in WordPress. Clean. Efficient. Untouchable. I was so proud of it.
Then it broke.
No warning. No big server crash. Just… errors. Vague, useless errors. `Syntax error`. `Unrecognized control character`. The JSON looked perfect in n8n. It left the station as a pristine package. But somewhere on the journey to WordPress, it was getting mugged, corrupted, and left for dead. The logs told me nothing. It was a ghost.
Chasing a Ghost in the Machine
I lost days to this. Literal days and nights. I tore my code apart, line by line. I rebuilt the API endpoints. I questioned my own skills, my logic, everything. Was I a fraud? Did I miss something basic? The data looked fine. The code looked fine. Yet it kept failing. Every single time.
The real killer, the invisible assassin, was so stupidly simple I almost threw my laptop across the room when I found it. It was a single character. The less-than sign. `<`.
The AI, in one of its outputs, had generated a temperature: `<19°C`. Benign, right? Wrong. WordPress, in its infinite and meddling wisdom, saw that `<` and thought, “Oh, an HTML tag! A security risk!” And it just… chopped the data string right there. It didn’t throw a warning. It didn’t log the truncation. It just murdered my JSON payload silently and completely. An overzealous security feature turned into a silent assassin.
Never Trust Incoming Data. Ever.
A simple fix wasn’t enough. This wasn’t just about one character. This was a violation of trust. If a simple `<` could bring down my entire system, what else was lurking in there? Zero-width spaces? Those curly “smart quotes” that copy-pasters love? Weird newline characters from different operating systems?
I was done patching holes. I was going to build a fortress.
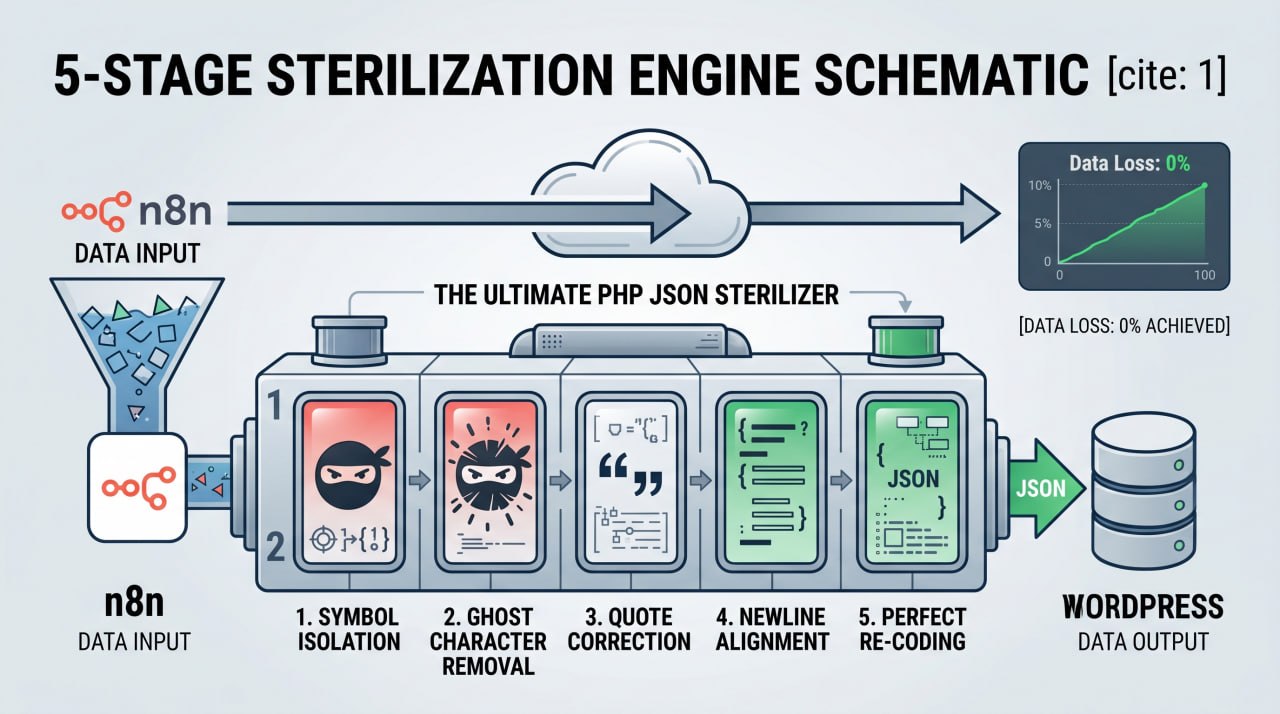
I spent the next 48 hours architecting what I call the “5-Stage JSON Sterilization Engine.” It’s a PHP function that treats every piece of incoming data like it’s radioactive. The visual I had in my head was one of those industrial diagrams. Dirty, corrupted data goes into a funnel at the top. Then it passes through five brutal stages of purification. One stage hunts down and kills invisible characters. Another one neutralizes smart quotes and weird symbols. The next few handle encoding and escaping so perfectly that nothing, absolutely nothing, can be misinterpreted. Like a little ninja that slices out every possible error before it can execute.
The output? Perfectly sterile, clean, 100% safe JSON. Data loss is zero. The pipeline is unbreakable now. It’s probably overkill, but I sleep at night.
The Ultimate 5-Stage PHP JSON Sterilizer
Here is the exact PHP parsing engine I built to completely sterilize the incoming n8n payloads before they ever touch the WordPress database. Feel free to steal this for your own infrastructure.
// 🚨 The Ultimate 5-Stage JSON Sterilizer 🚨

// Stage 1 & 2: Quote Correction & HTML Entity Decoding
// Forces WordPress to revert any aggressive HTML encoding (like < or smart quotes)
$clean_content = html_entity_decode($raw_content, ENT_QUOTES, 'UTF-8');

// Stage 3: Symbol Isolation (Payload Extraction)
// Scans and isolates ONLY the exact JSON payload, ignoring any surrounding garbage text
$start = strpos($clean_content, '{');
$end = strrpos($clean_content, '}');

if ($start !== false && $end !== false) {
    $json_str = substr($clean_content, $start, $end - $start + 1);

    // Stage 4: Ghost Character Removal (The Invisible Assassin Killer)
    // A ruthless Regex that strips out all zero-width spaces, control characters, and anomalies (ASCII 00-1F, 7F)
    $json_str = preg_replace('/[\x00-\x1F\x7F]/', '', $json_str);

    // Stage 5: Perfect Re-coding
    $data = json_decode($json_str, true);

    if (json_last_error() !== JSON_ERROR_NONE) {
        $json_error_msg = json_last_error_msg(); // Failsafe logging
    }
}
The deadliest bugs aren’t the ones that scream at you in the error logs. They’re the invisible assassins that your own system creates. Don’t trust your tools. Don’t trust the platform. Suspect every byte of data that comes through the door. The only path to a stable backend is through absolute, ruthless sterilization.
“Don’t just fix the error; build a system where that class of error can never exist again.”